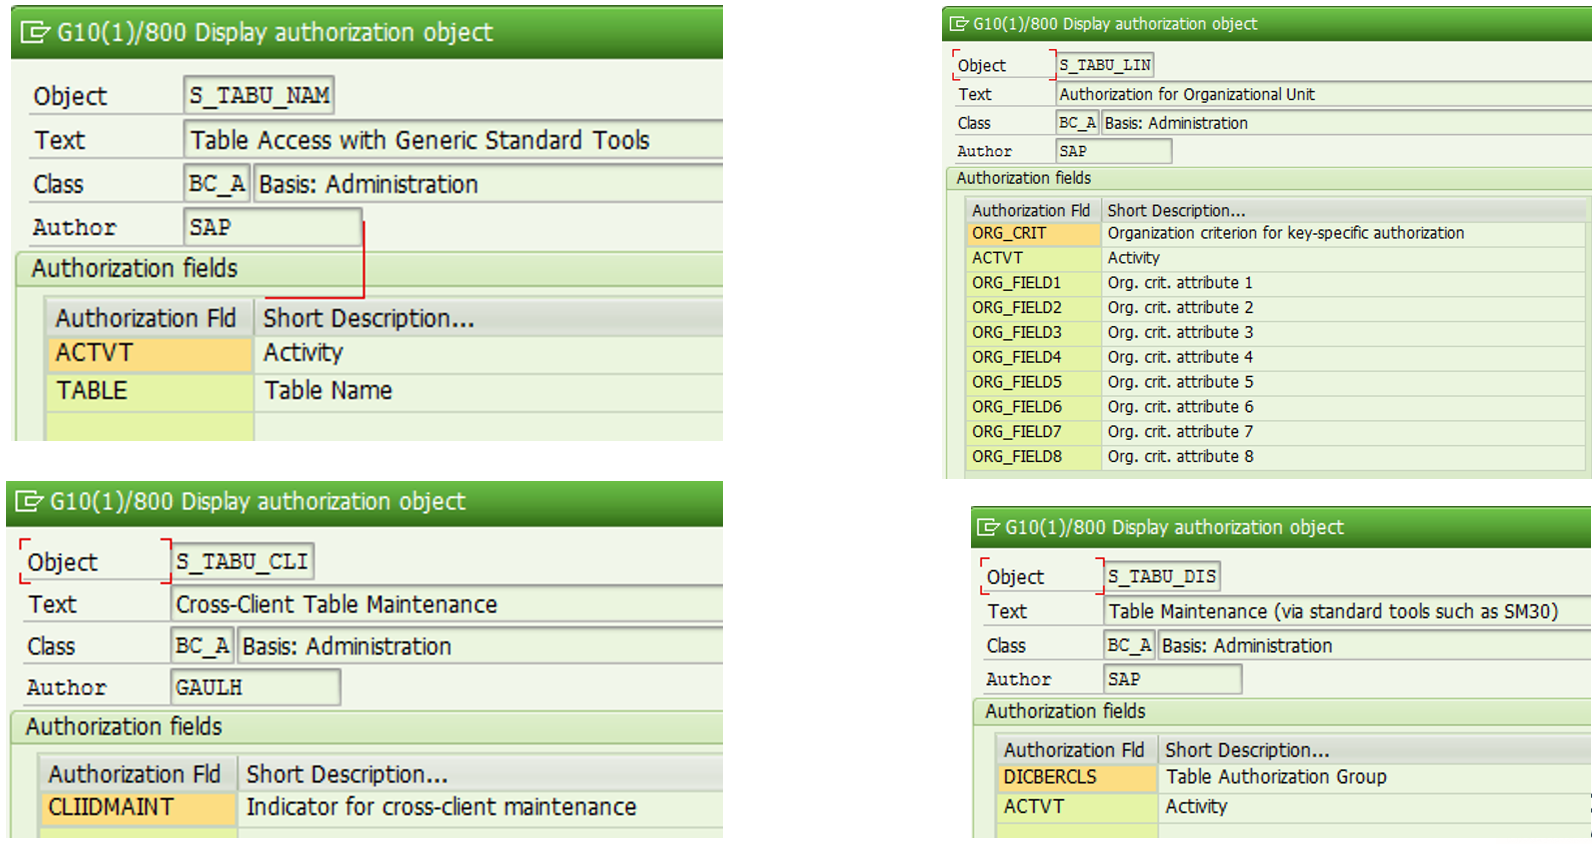
For those that don't know SAP's authorization aspects this title might be just a tongue-twister.
On the contrary for those who manage authorizations in SAP these are very well-known authorization objects. How should you go about managing them?
For those that don't know SAP's authorization aspects this title might be just a tongue-twister.
On the contrary for those who manage authorizations in SAP these are very well-known authorization objects. How should you go about managing them?
Topics: se16, s_tabu_dis, s_tabu_rfc, s_tabu_nam, sql
Who said that in order to have powerful systems you need to have many resources?
How can a small enterprise be compete with a big corporation?
Topics: sap cyber security, siem, threat detection, security bridge
The aim of the SoD is to make sure that only people with the right are of competence have access to sensitive transactions.
Topics: Segregation of duties, Security Analyzer
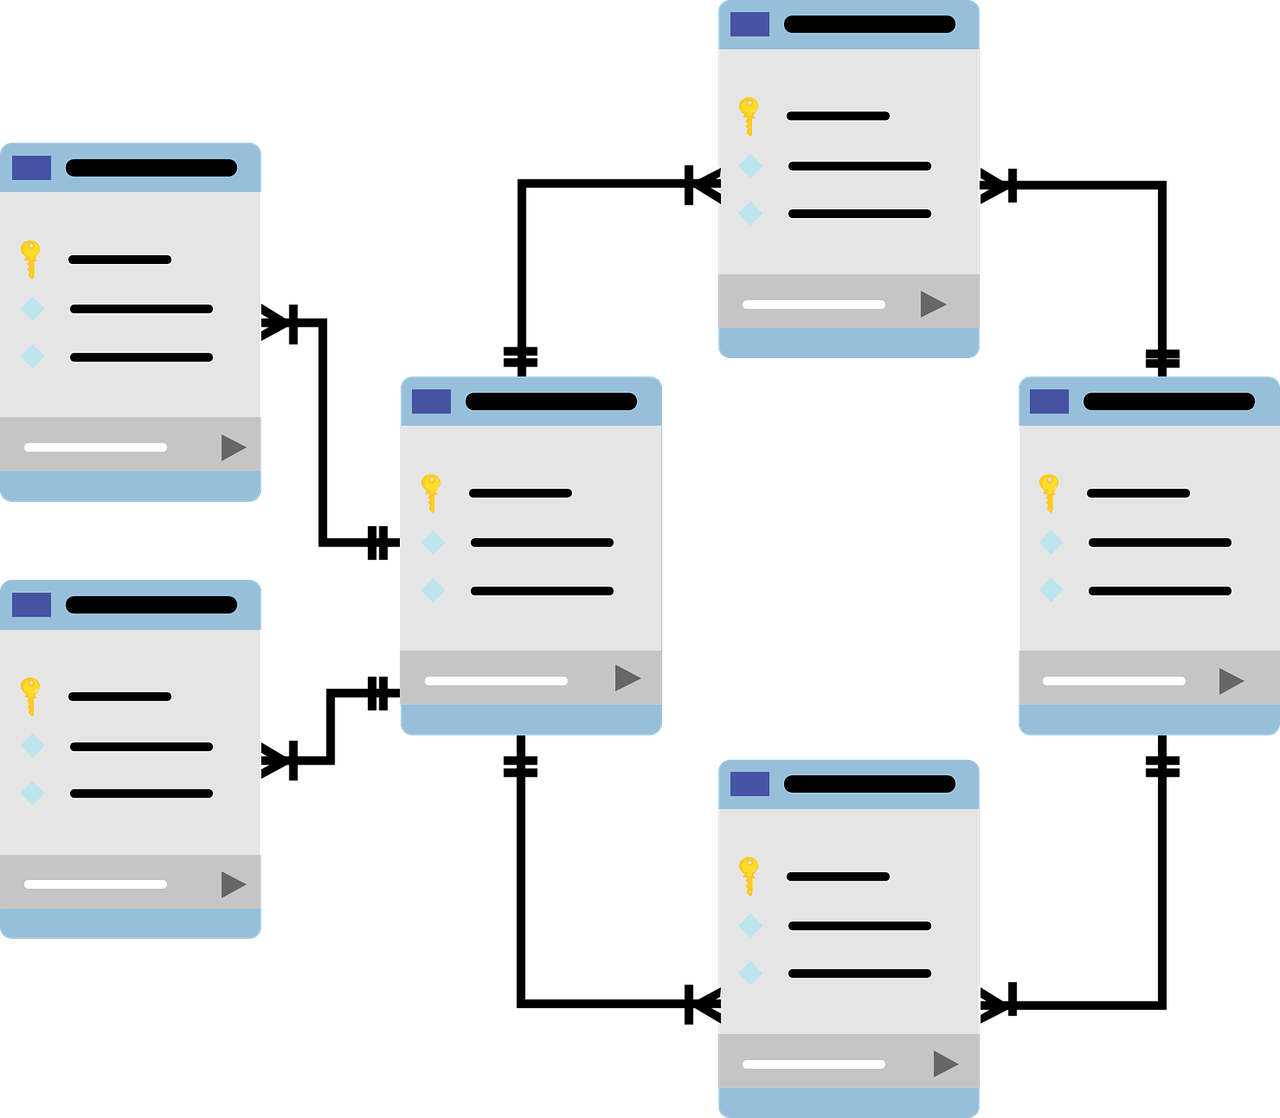
SAP contains hundreds of thousands of tables. In some cases the direct access to these tables allows one to retrieve data faster. Below a list of tables for each defined area:
Topics: SAP ECC, sap standard role, Profiles, SAP Table
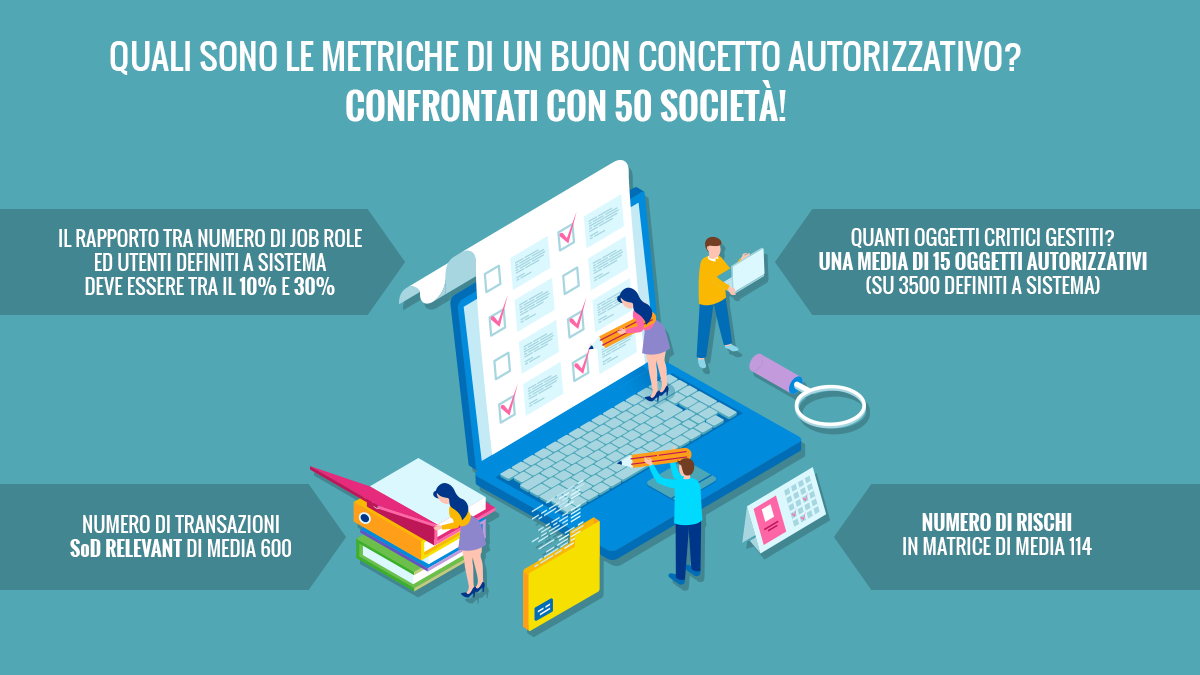
How does one know if you have set up a good authorization concept in SAP??
What are the metrics and how to best exploit them? Does a SAP Security Score exist?
Topics: User Access Management, autorizzazioni sap, sap custom, Statistiche security SAP
Why is that all the decisions taken following authorization assignments requests fall under the IT department?
Topics: Segregation of duties, sap access control
For reasons of internal policies or regulations it may be necessary to make some data inside of SAP anonymous. There are many ways to do this. The first elements we need to consider are:
Topics: SAP GDPR, UI logging, UI Masking
SAP updates are frequent. SAP releases feature updates to its products but also new features or patch security.
Is it really possible that external consultants do not have any access to SAP production systems?
Clearly there are various case studies, occasional or ongoing consultants, for example for maintenance contracts.
Is it really necessary to release an access to the production systems even in this last case? Can we control what happens and why it is requested?